“NIS-2 ASSESSMENT & ROADMAP”
Karer Consulting brings structure and clarity to the evolving regulatory landscape around NIS‑2, ISO 27001 and related cybersecurity obligations. Our focus is not on theoretical compliance, but on translating regulatory requirements into clear priorities, executable work packages and a realistic roadmap.


Initial Situation
Our client – a global medical technology company – develops, manufactures and distributes medical devices. As a European company headquartered in Germany, the group is required to comply with the NIS-2 Implementation and Cybersecurity Strengthening Act (NIS2UmsuCG).
In addition to NIS‑2, the client aims to establish the foundation for a future ISO 27001 certification and to address further industry‑specific standards, such as ISO 81001‑5‑1.
The key challenge was to review, prioritize and integrate these requirements into a single, coherent ISMS, while considering existing processes, documentation, and IT security measures already in place.

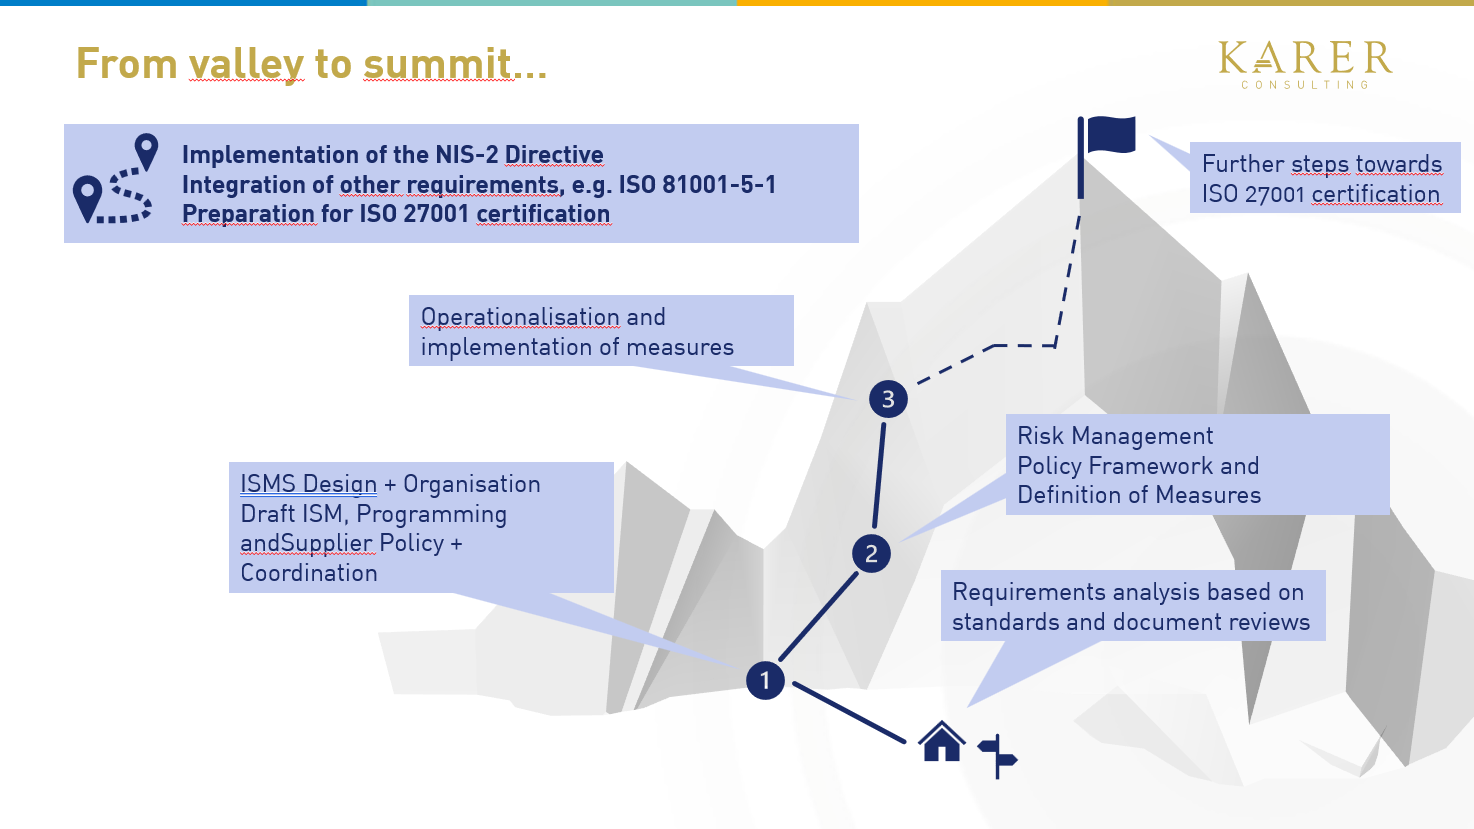
Karer Consulting was engaged to leverage its expertise in regulatory requirements, information security and NIS‑2 to design a comprehensive roadmap for implementation. The assignment explicitly focused on pragmatic execution: existing processes and compliance concepts were reviewed, aligned with regulatory requirements and translated into concrete work packages that could be realistically implemented within the organization.
Measures
- Early involvement of all relevant stakeholders, including management, IT and business units, to establish awareness and ownership
- Structured review and mapping of all applicable regulatory requirements, with a clear focus on NIS‑2 and ISO 27001
- Derivation of concrete and prioritized implementation measures
- Regular checkpoints to ensure transparency on progress, risks and next steps
KC Process Model
Karer Consulting started with a structured assessment workshop together with the client’s experts and management. This workshop provided a comprehensive overview of the NIS‑2 Directive, its implications and its relationship to ISO 27001 certification.
Beyond knowledge transfer, the workshop served to raise awareness of new regulatory obligations and align all participants on common objectives. Building on this foundation, Karer Consulting performed a systematic gap analysis.NIS‑2 and ISO 27001 requirements were compared against existing documentation, processes and the security measures actually implemented in day‑to‑day operations. The identified gaps were translated into client‑specific measures, carefully prioritized and structured into a compliance roadmap.
Strong emphasis was placed on best practices, feasibility and practical implementation, rather than purely formal compliance. Finally, Karer Consulting developed the initial set of overarching ISMS policies and guidelines and supported their implementation together with the client.


Lennart Rasche
Telephone: +49 751 185 275 0
E-Mail: sales@karer-consulting.com
www.karer-consulting.com